Security, by design.
Apate is designed to add minimal attack surface to the networks it watches. This page summarizes our security posture, how we handle data, and where we stand on formal attestations - stated honestly, not overclaimed.
Built to add minimal attack surface.
Non-destructive by default
It won't block, quarantine, push config or modify any device, so it can't be turned into a control plane. Any active or on-path mode is opt-in and off by default.
No inbound exposure
Sensors push outbound only. No listening port is opened on monitored segments - it works even from OT and air-gapped networks.
No endpoint agent
Network-level. No driver or agent on your endpoints, so no added endpoint attack surface and no fleet-crash risk.
Self-hosted
Runs on your infrastructure. No mandatory third-party cloud; your telemetry never has to leave your environment.
Encrypted & authenticated
TLS in transit, token-based RBAC, and a tamper-evident audit log of every action.
Data-minimized
Posture and metadata only - never packet payloads, files or credentials. Storage is bounded, not an ever-growing data lake.
Transparent about where we are.
Design-partner engagements run under NDA while formal attestations are completed.
In place today
Opt-in active modes, TLS transport, RBAC, audit logging, on-prem data residency and data minimization.
In progress
SSO (SAML/OIDC), code-signed builds, an independent penetration test, a DPA and this Trust Center.
Planned
SOC 2 Type II and ISO 27001, high-availability and multi-tenant deployment, and cross-platform sensors.
Frugal with data, by design.
A sensor's snapshot carries posture and metadata only. Because Apate is content-free, large parts of a standard vendor security questionnaire simply don't apply - which shortens review rather than lengthening it.
- Collected: posture score & grade, finding counts, device inventory metadata, event metadata
- Never collected: raw packet payloads, files, credentials or user content
- Encrypted in transit (TLS); at rest it lives in your own store, under your controls
- You choose region and retention - straightforward for GDPR / data-residency
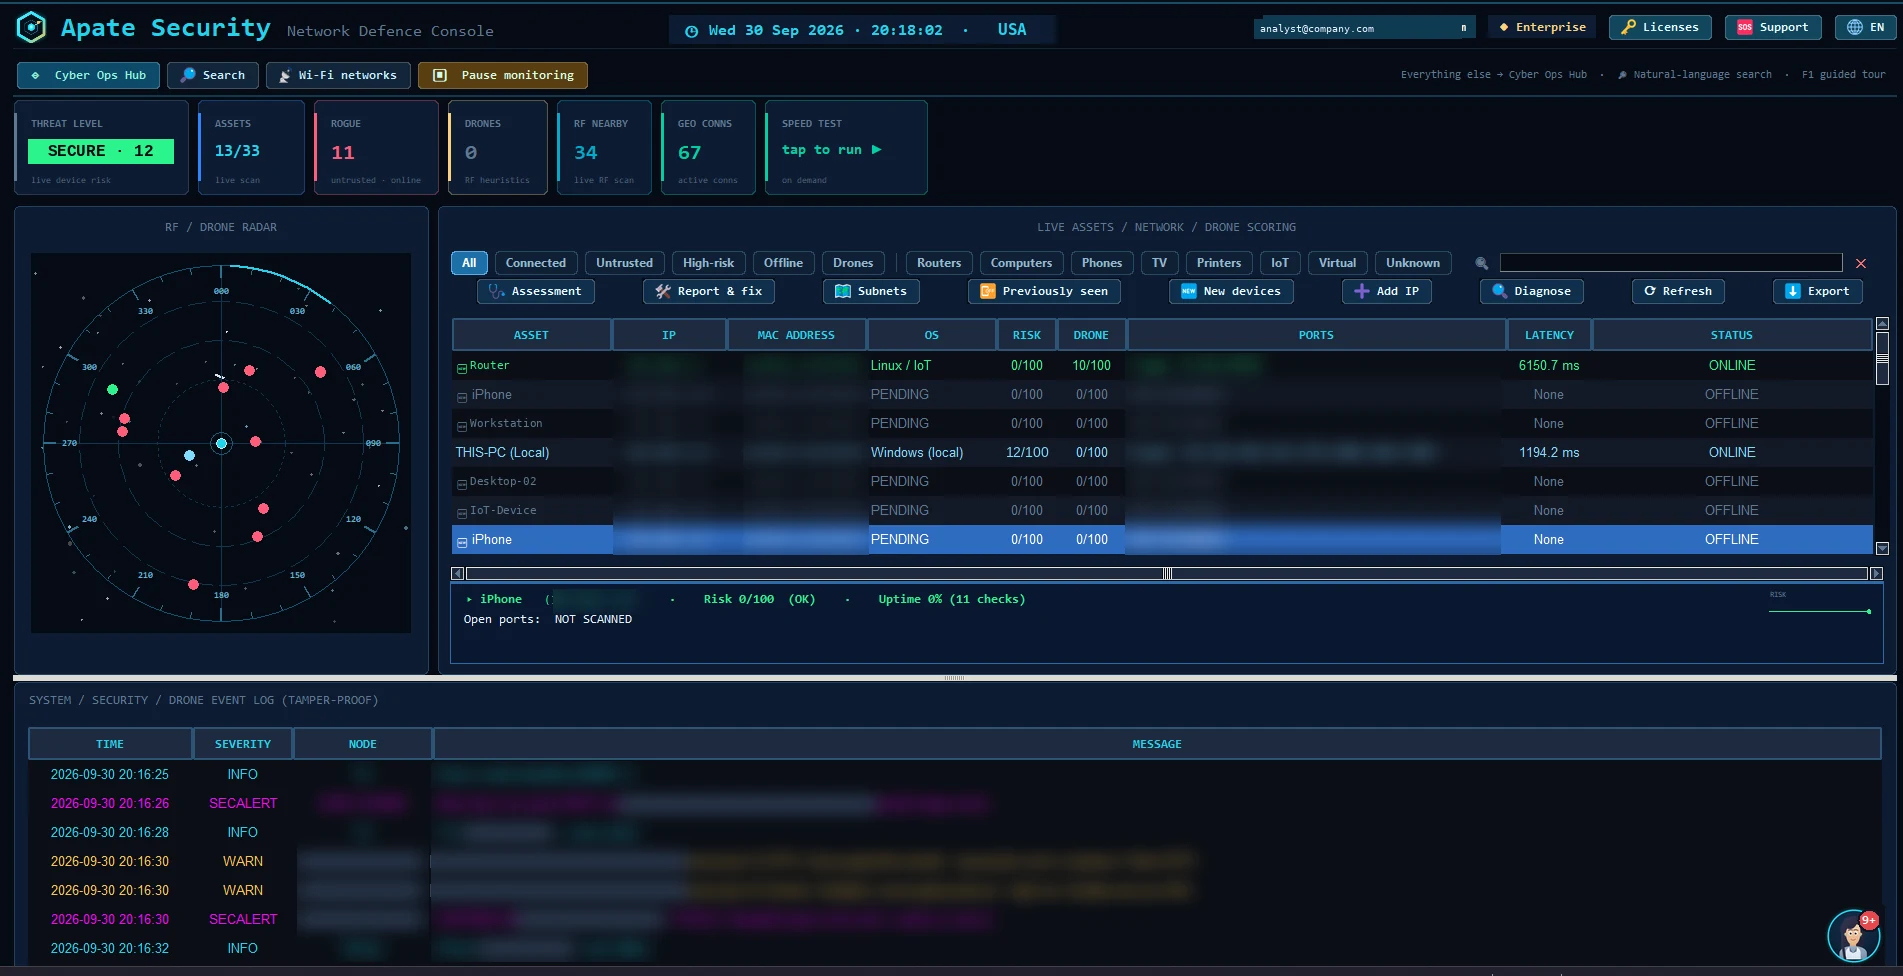
Least privilege, fully accountable.
Role-based access & SSO
Three least-privilege roles - admin, viewer and write-only ingest. SSO via OIDC (Okta / Entra ID) maps your IdP group to the Apate role; MFA is enforced by your IdP.
Audit trail
Every write, privileged read and auth failure is logged with time, role, a non-reversible token fingerprint, path, status and source IP.
No required subprocessor
Self-hosted - your data does not pass through Apate-operated cloud services. Optional IP-intelligence lookups run only to providers you enable with your own keys.
Outbound-only data flow
Sensors push posture snapshots outbound over TLS to your own collector. Nothing dials into a monitored segment.
Report a vulnerability.
We welcome responsible disclosure. Email security@apatesecurity.com with details and steps to reproduce; we'll acknowledge and work with you on a fix. Please don't publicly disclose until we've had a reasonable chance to remediate.